Skip the $15k Pentest — Run One Tonight for $47
Your last penetration test cost $15,000. It took six weeks to schedule, two weeks to execute, and by the time the 80-page PDF hit your inbox, three new CVEs had already dropped against your stack. That's the dirty secret of traditional pentesting. You're paying for a snapshot that's already stale. Here's the alternative: install a CLI tool, define your scope, and have a full penetration test running before midnight. Total cost: $47 a month.
How much does a penetration test actually cost?
The average penetration test runs between $5,000 and $50,000 per engagement. Web application tests start around $5,000. Network penetration tests charge $150 to $1,000 per device. Enterprise-wide assessments regularly clear $30,000.
And that's just the sticker price. Factor in the hidden costs: weeks spent vetting firms, back-and-forth on scope documents, waiting while testers juggle other clients. Most organizations wait four to six weeks between signing the contract and seeing results.
Here's why that delay is dangerous: 60% of breaches exploit known vulnerabilities where a patch already existed (Verizon DBIR 2025). Every week you wait for a pentest report is another week those vulnerabilities sit exposed.
Why do traditional pentests cost so much?
Three things drive the price tag.
- Skilled testers are expensive. Certified penetration testers command $150 to $300 per hour. A thorough web application test takes 40 to 80 hours of their time. Do the math: that's $6,000 to $24,000 before anyone writes a single line of the report.
- Every engagement is bespoke. The firm scopes your environment, builds custom test plans, runs the assessment, writes the report, then briefs your team. That's a lot of billable hours that don't involve actual testing.
- You're competing for their calendar. Reputable firms book out months ahead. Urgent timelines cost a premium. Need a pentest before next quarter's compliance audit? Get in line.
The result: most companies test once a year. Some test quarterly. Almost none test continuously, because at $15,000 a pop, continuous isn't an option.
What if you could run a pentest tonight?
Something changed in the last two years. AI agents can now execute the same reconnaissance, vulnerability scanning, and exploit verification that human testers perform, in minutes instead of weeks.
No scheduling. No scope meetings. No waiting for a PDF.
You define the targets. The agent handles subdomain enumeration, port scanning, CVE detection, and proof-of-concept verification. It generates a report when it finishes. You run it again tomorrow when your code changes.
The median time to exploit a new CVE is now under five days (Mandiant M-Trends 2025). Over 28% of exploited vulnerabilities get weaponized within 24 hours of disclosure. Annual pentesting can't keep pace with that math.
How does automated AI penetration testing work?
Automated AI pentesting follows the same methodology manual testers use. It just finishes before your morning standup.
- Define scope. You specify which domains, IPs, and services are authorized targets. Scope-guard controls block anything outside these boundaries.
- Reconnaissance. The AI agent maps your attack surface automatically: subdomains, open ports, running services, exposed APIs, and technology stacks.
- Vulnerability scanning. The agent runs CVE checks against discovered services using Nuclei templates and known vulnerability databases.
- Exploit verification. Instead of just flagging potential issues, the agent attempts proof-of-concept exploitation to confirm which vulnerabilities are actually exploitable. This kills false positives.
- Report generation. Results export to Markdown, JSON, PDF, or SARIF, ready for your ticket system or compliance workflow.
The entire process takes minutes to hours depending on scope. Not weeks.
The real cost comparison
| Traditional Pentest | AI Pentesting (Redcell) | |
|---|---|---|
| Cost per test | $5,000 to $50,000 | $47 to $199/month (unlimited) |
| Time to start | 4 to 6 weeks | Tonight |
| Time to results | 1 to 2 weeks | Minutes to hours |
| Test frequency | Annual or quarterly | On every deployment |
| Report format | 80-page PDF | Markdown, JSON, PDF, SARIF |
| False positive handling | Manual review | PoC verification built in |
Disclosure: We build Redcell.
That's the difference between renting a consultant and owning the capability. At $47 a month, you could run a penetration test every single day for an entire year and still spend less than one traditional engagement.
FAQ
Is automated pentesting as thorough as manual testing?
Automated testing excels at breadth: it scans every subdomain, every port, every known CVE, consistently. Human testers excel at depth: chained exploits, business logic flaws, and creative attack paths. The two are complementary. But most organizations get no regular testing at all because manual testing is too expensive. Running automated scans continuously and saving manual tests for targeted deep-dives covers more ground than a single annual engagement.
Can a startup or small team actually use this?
Yes. The biggest barrier to penetration testing has always been cost. At $47 a month, a three-person startup gets the same recon and vulnerability scanning that used to require a five-figure budget. Install from your terminal and you're running scans within minutes.
What's the difference between a vulnerability scanner and automated pentesting?
Vulnerability scanners flag potential issues. Automated pentesting goes further: it discovers your full attack surface through reconnaissance, scans for vulnerabilities, then attempts proof-of-concept exploitation to verify which findings are real. That verification step is what separates a scanner from a pentest.
Stop paying for stale snapshots
48,174 new CVEs were published in 2025. That's 131 every single day. Your once-a-year pentest can't cover that. And waiting six weeks for a report means you're flying blind during the window that matters most.
Stop paying $15,000 for a security snapshot that expires before you read it. Run your own penetration test tonight:
curl -fsSL https://redcell.sh/install.sh | sh
Put AI defensive automation into your terminal
RedCell gives defensive engineers autonomous reconnaissance, CVE verification, and triage reports with strict scope guard.
Read next
Your Pentester Costs $200/hr. This One Costs $1.50/Day.
Automated AI pentesting runs recon, exploits, and reports 24/7 — for less than your morning coffee.
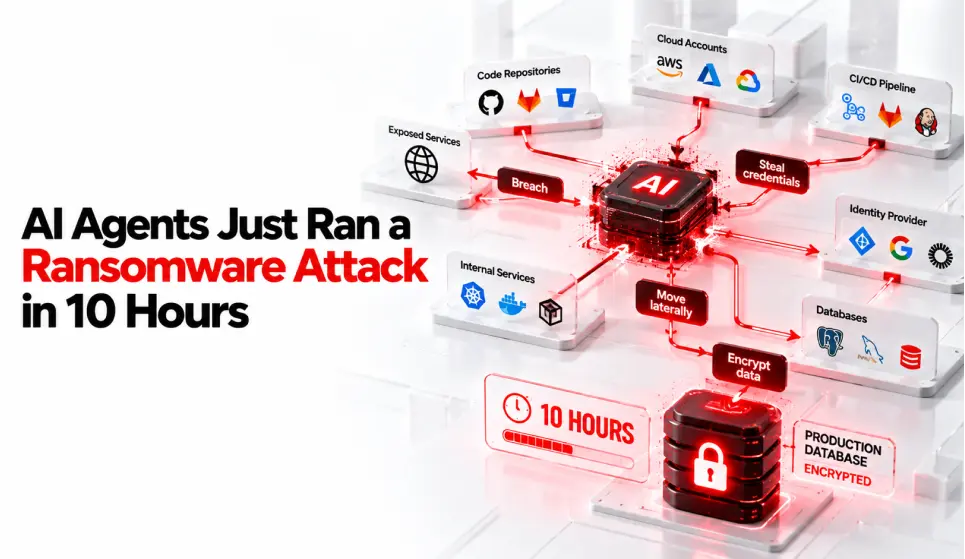
AI Agents Just Ran a Ransomware Attack in 10 Hours
An AI agent completed a full ransomware attack in under 10 hours — no human operator needed. Here's what happened and how to test whether your defenses can keep up.
How to Scan the Citrix NetScaler Zero-Days Without Breaking Scope
CVE-2026-88771 and CVE-2026-88772 hit 22,000 exposed NetScaler instances. Learn how to map, scan, and verify both zero-days inside strict scope using an AI pentesting agent.